


What cyber security companies offer
| Service | What you get | Good for |
|---|---|---|
| Security review | A check of your accounts, devices, email, backups and network, with a prioritised list of fixes | Almost every business, as a starting point |
| Improvement work | Two-step login, Microsoft 365 security settings, device protection and firewall changes, done for you | Fixing what the review finds |
| Ongoing security management | Updates, monitoring and regular checks as a monthly service | Businesses without in-house IT |
| Penetration testing | An authorised, simulated attack on a system, with a report of what got through | Websites, apps and networks that hold sensitive data |
| Staff awareness training | How to spot phishing emails, fake invoices and other scams | Every team, since most attacks start with a person |
| Incident response | Help to contain an attack, recover systems and work out what happened | When something has already gone wrong |
Most small businesses don't need every service. A good provider starts by finding out where your real risks are.
What to sort out first
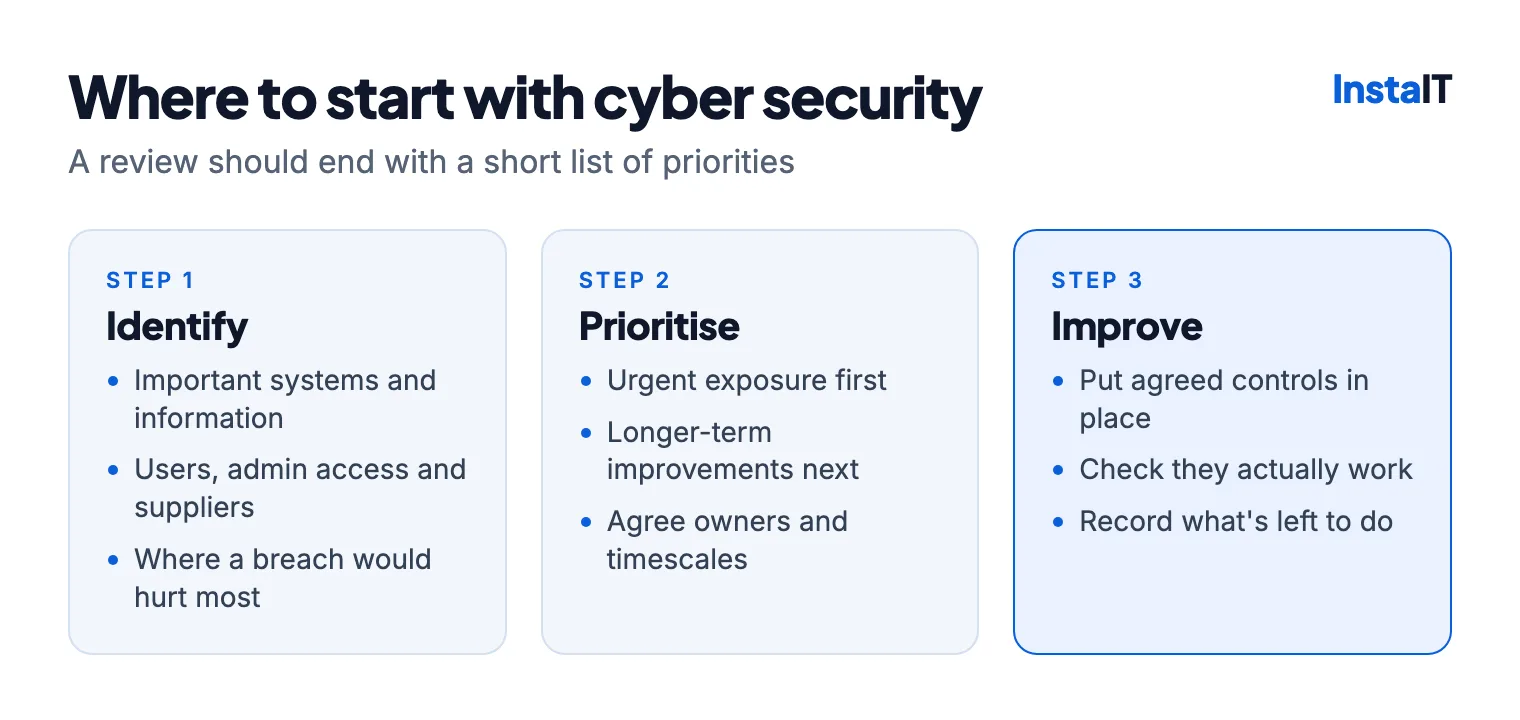
For most small and medium businesses, the biggest gains come from the basics, done properly:
- Two-step login (MFA) on email, Microsoft 365 and every admin account.
- Prompt updates for computers, phones, firewalls and websites.
- Protection on every device, with alerts that reach someone who acts on them.
- Email security that filters phishing and fake invoices.
- Backups stored separately, and a restore you've actually tested.
- Staff who know what a scam looks like, and who to tell when something seems wrong.
Our cyber security checklist for small businesses walks through each one, and the National Cyber Security Centre's advice for small businesses is a good free resource.
Local or remote?
Most security work, such as reviewing Microsoft 365 settings, rolling out two-step login or checking device protection, is done remotely. On-site visits matter for firewalls, network changes, Wi-Fi and anything involving equipment in your office.
A provider in Ireland also understands the rules you work under: GDPR and the Data Protection Commission, and the EU's NIS2 cyber security rules, which cover many medium and large organisations in certain sectors and can affect their suppliers too.
Questions to ask
- Where would you start with a business like ours? Expect a review of your current setup before any product is recommended.
- What will we get at the end? A written report with priorities, owners and costs, in plain English.
- Who will do the work, and what are their qualifications? Ask about relevant certifications and experience with businesses your size.
- Will you work with our existing IT provider? Security changes often touch systems someone else looks after.
- How will you handle our data and access? Ask how their own accounts are protected, and for a written agreement covering any personal data they can see.
- What happens if we're attacked? Who you call, how quickly they respond and whether that's included.
- What's ongoing, and what's one-off? Separate the review and fixes from any monthly service.
Red flags
- Promises that you'll be "100% secure". No provider or product can remove every risk.
- Selling a product before anyone has looked at your setup.
- Scare tactics and pressure to sign the same day.
- No written report, or one full of jargon with no priorities.
- Wanting permanent admin access to everything with no record of who uses it.
If you've been attacked
- Get help straight away from your IT or security provider, and don't keep using a device you think is compromised.
- Change passwords from a device you trust, starting with email and admin accounts, and check that two-step login is on.
- Report it. The National Cyber Security Centre handles cyber incident reports, and fraud should be reported to An Garda Síochána.
- Check whether personal data was affected. If it was, you may need to tell the Data Protection Commission within 72 hours.
How InstaIT can help
Our cyber security services start with a review of your identities, admin access, Microsoft 365 setup, devices, email, updates, backups and relevant network controls. We then agree a practical list of priorities and can carry out the improvements in phases that suit your budget and the way you work: two-step login, Microsoft security settings, device protection, email security, firewall reviews, backup readiness and staff guidance.
Much of the work can be done remotely, with on-site visits in Cork when they're needed. We don't promise that every risk can be removed, and we'll tell you when a specialist, such as a penetration tester, is the right next step.
CYBER SECURITY IN CORK AND IRELAND
Not sure where to start?
InstaIT can review your current setup and give you a short, prioritised list of what to fix first. See our cyber security services.
Ask about a security review